

Cyber Security
Every system on the internet is probed by automated attackers around the clock. We scan yours, close the gaps we find, test the defences and keep them up to date.
Trusted by global brands
The Scale of Automated Attack
Most attacks are not aimed at you in particular. They are automated, they run all day, and they try every system they can reach.
What Attackers Look For
Any system with a login page is already being tested by somebody else, and this is the kind of traffic a live system sees in a single minute.
What they are looking for
- Software that is behind on its updates
- Old logins that nobody removed
- Admin pages open to the whole internet
- Logins with no limit on attempts
- Backups left where they can be fetched
- Logs that nobody reads
What We Test and Fix
Choose an area to see what you receive. Each can be taken by itself, although they work best as one routine.
Everything exposed is checked
- Servers, applications and APIs scanned
- Out-of-date software and libraries listed
- Exposed admin pages and open ports found
- Findings ranked by real risk
A scan is the quickest way to learn where you stand, which is why most engagements begin with one.
Attacked on purpose, by people on your side
- Manual testing that goes beyond scanners
- Attacks on logins, sessions and permissions
- Abuse of business rules, such as prices or roles
- A written report with the proof and the fix
The scope and the time window are agreed in writing first, so nothing is touched that should not be.
Gaps closed and kept closed
- Operating systems and software patched
- Encryption, headers and access rules tightened
- Old accounts, keys and passwords cleared out
- Backups proven by restoring them
Because we are engineers first, the people who find a weakness are the people who fix it.
Defences rehearsed before they are needed
- Simulated bot floods and login attacks
- Alerting tested to see who is actually told
- Recovery drills from a clean backup
- Monitoring that continues, with a monthly report
A defence that has never been tested is only a hope, so we run the drill while nothing is at stake.
Security as a Routine
New weaknesses are published every week, which means a system that was safe at launch will not stay safe unless somebody keeps looking.
A report a board can read
Findings are written in plain English with the risk, the evidence and the fix, so that leadership can make decisions from them.
Fixed by the people who found it
We build and run live systems ourselves, so a finding is closed with working code and not left as a recommendation.
Verified by Anthropic for defence work
BY BANKS is verified under Anthropic's Cyber Verification Program at the Defense Access tier, which gives vetted organisations access to its most advanced AI models for finding and fixing weaknesses.
Selected Work
Platforms and products we have built and keep secure, each with its own case study.
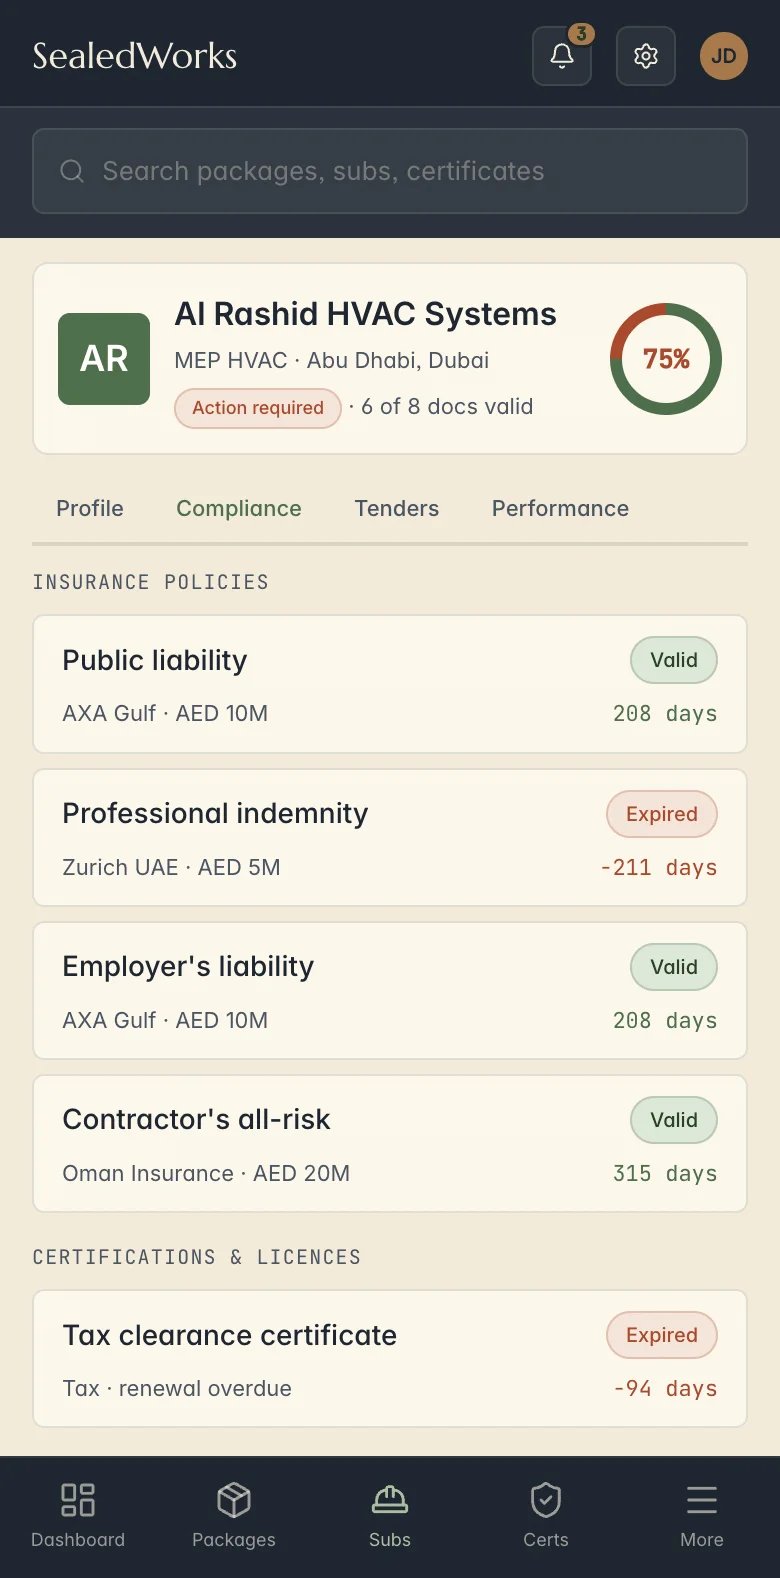
Sealed bids and audit trails for GCC contractors.
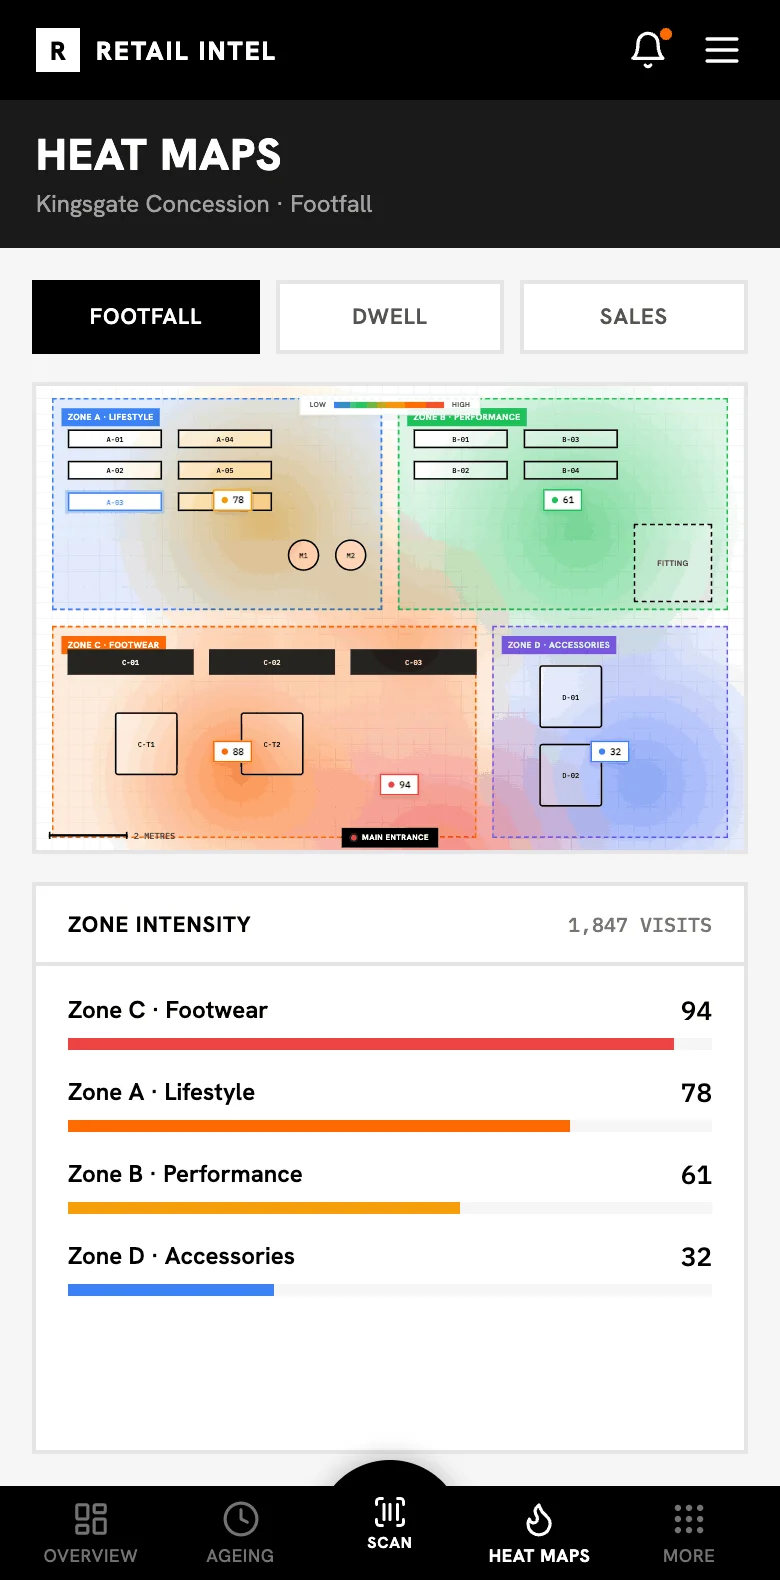
Full visibility from delivery to stockroom to shop floor to sale.
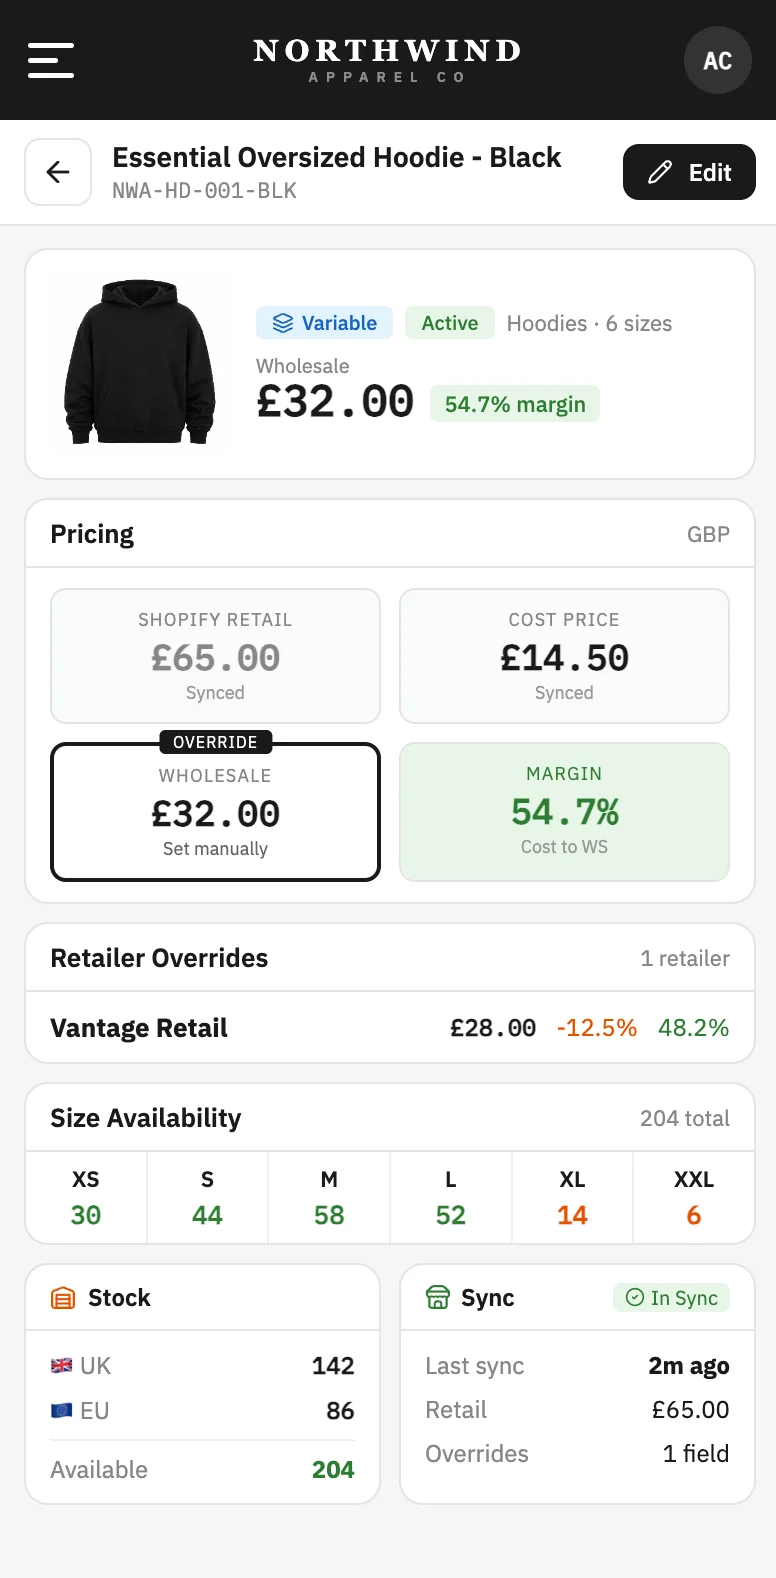
A Shopify-synced platform that runs an entire wholesale operation.
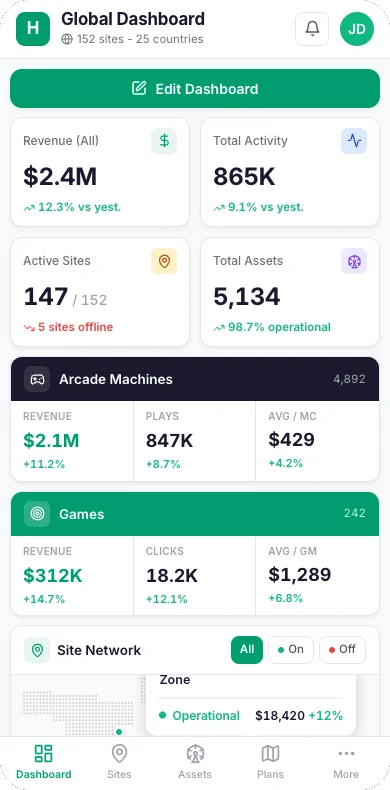
Centralised control for 150+ attractions across 25+ countries.
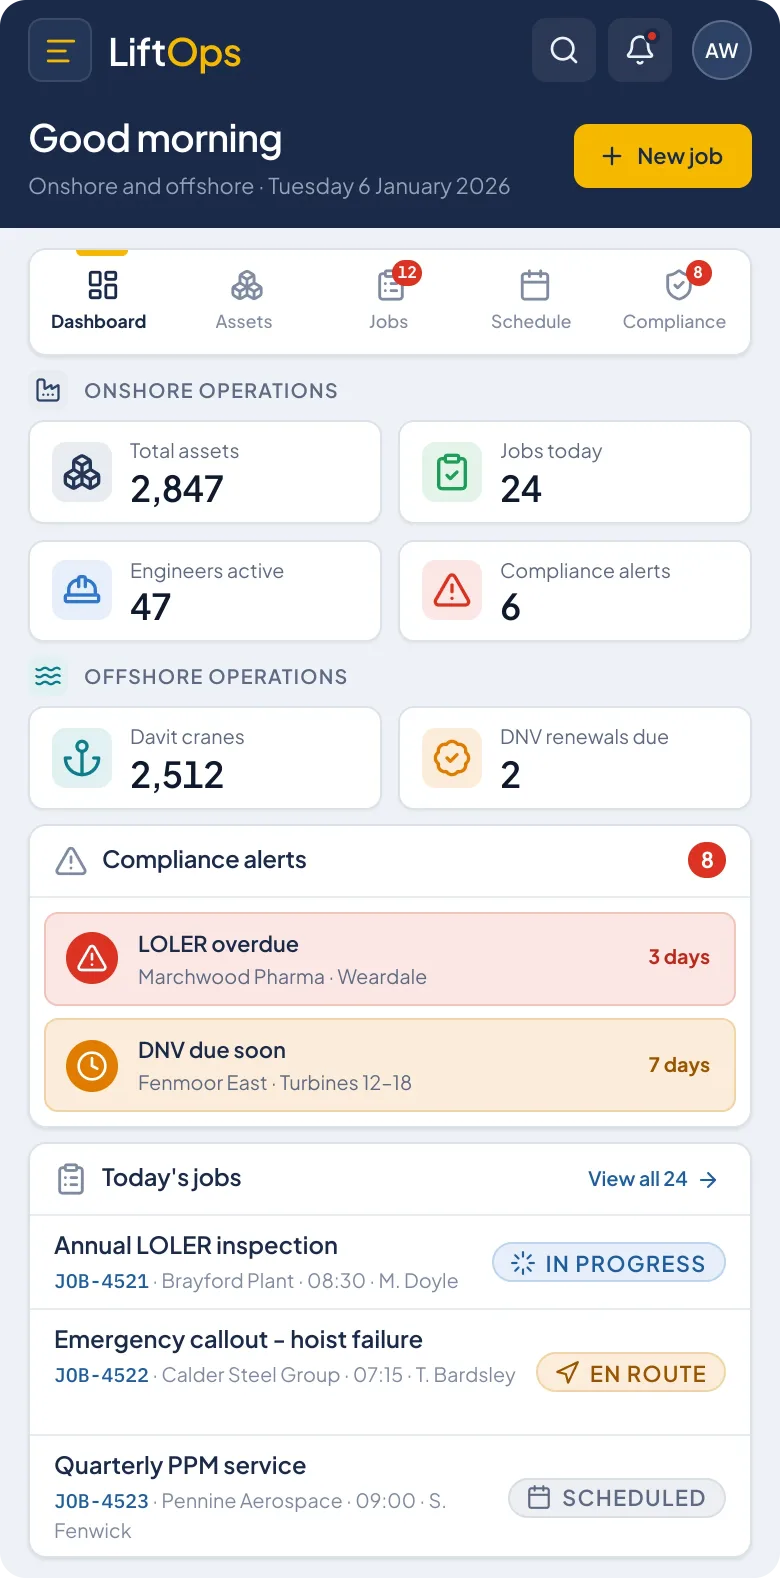
Field-first operations for 5,300+ assets, onshore and offshore.
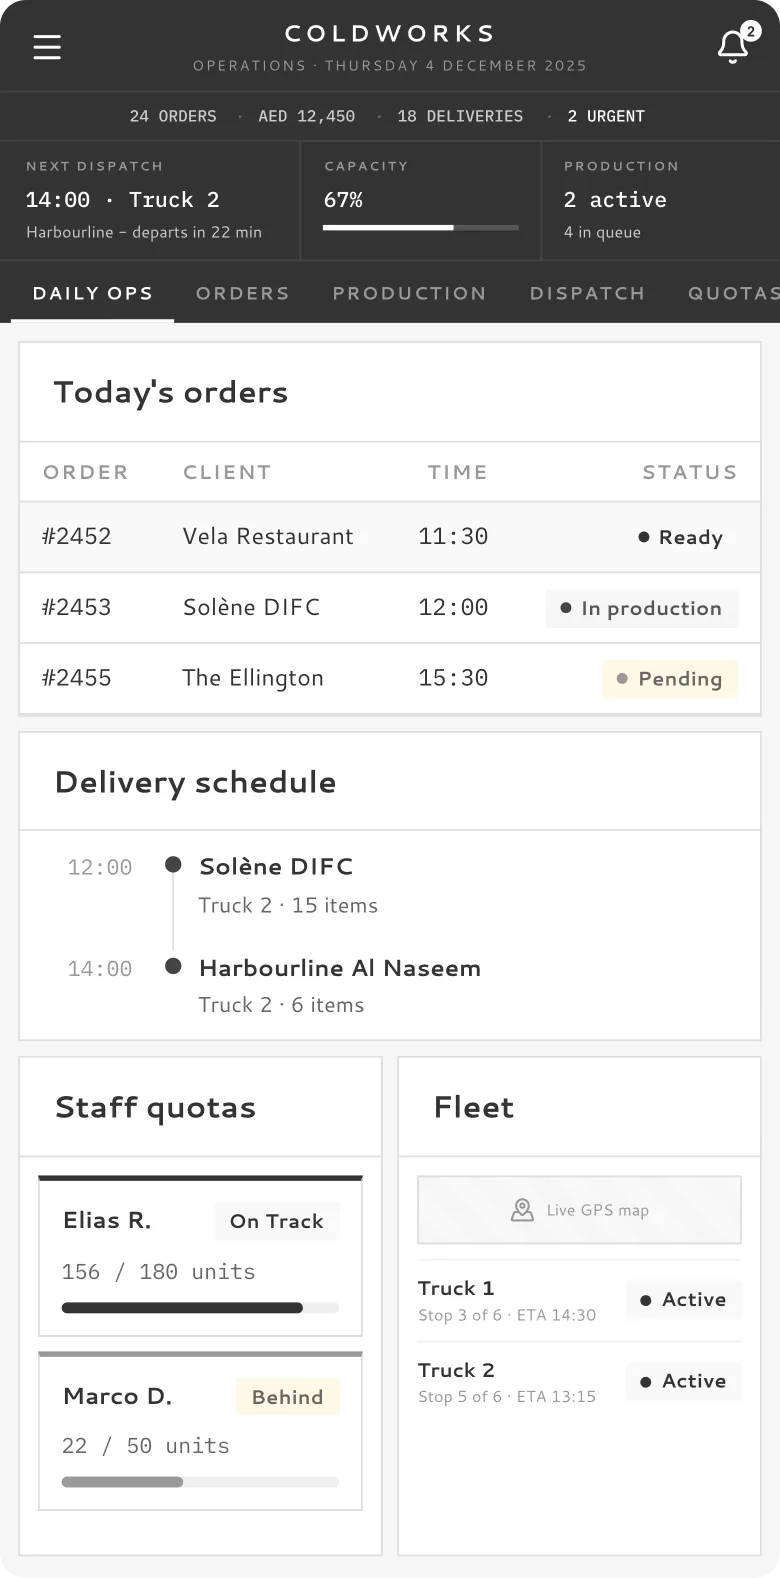
Fifteen modules, from the production floor to the customer's door.
A complete retail operating system, replacing the off-the-shelf stack entirely.
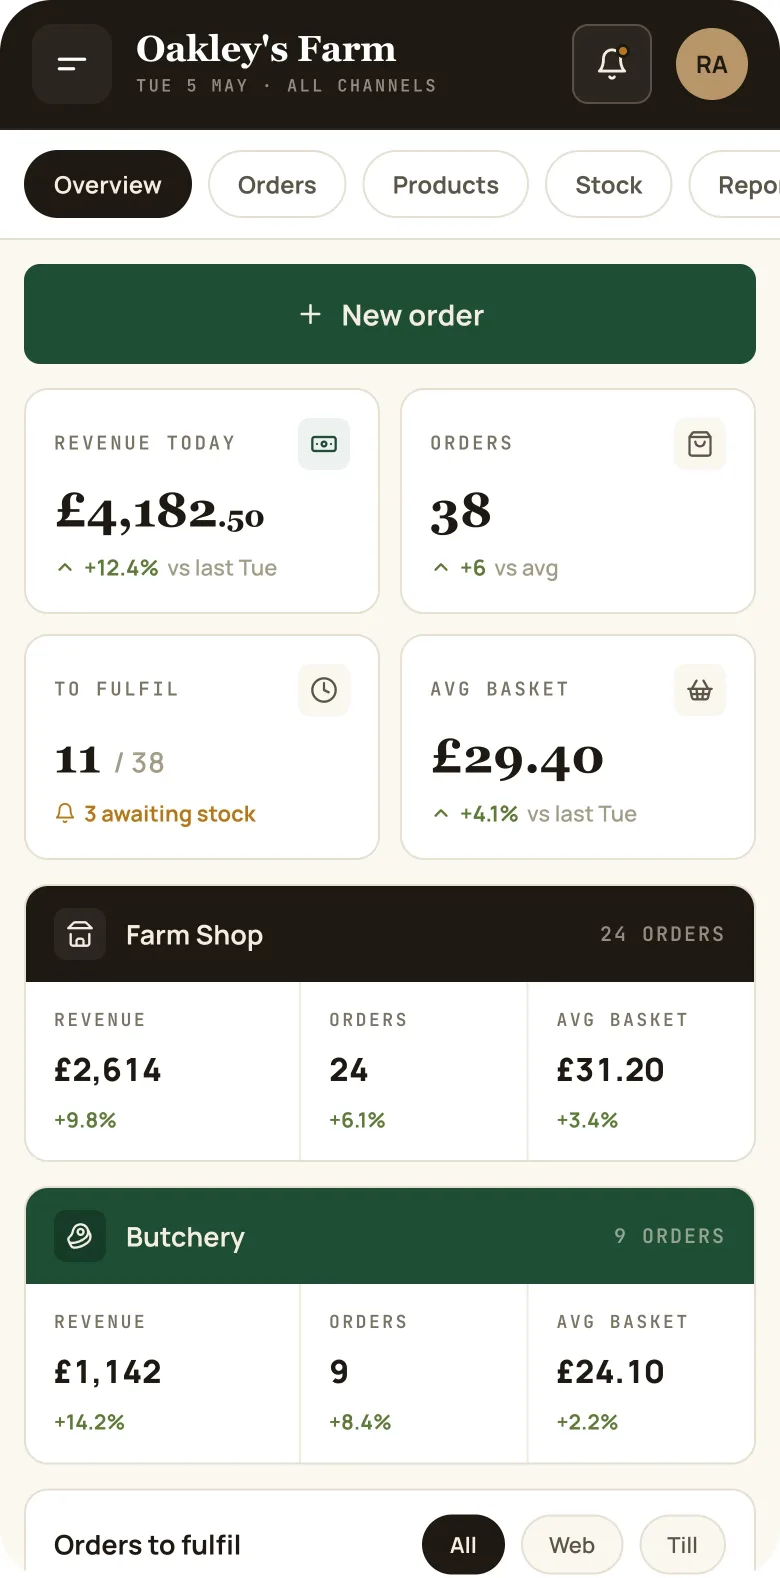
A product we built, launched and run ourselves.
Senior Engineers Who Run the Whole Project
The engineer who tests your system is a senior engineer who builds and runs live platforms, with no juniors and no offshore handovers.
manager
manager
 Paul Banks
Senior engineer and founder
Paul BanksSenior engineer and founder
One engineer, start to finish
The same senior engineer reports to your board, leads the design reviews and change management, engineers the build, and carries out the testing and security checks.
Two or three on larger projects
When a project needs more hands, two or three senior engineers now deliver what used to take a team of ten or more.
We build our own products too
Our advice is tied to risks we take with our own money.
Frequently Asked Questions
Plain answers before you get in touch.
Will testing disrupt our live system?
No. Scans are tuned to be safe for live systems, and any test that carries risk is agreed in writing and run in a quiet window or against a copy.
Can you secure a system you did not build?
Yes. Much of this work is on systems built by other teams, and we begin by reading the code and the hosting as they stand.
How often should this be done?
A full test at least once a year and after any major change, with scans and updates running every month in between.
What do we receive at the end?
A ranked report in plain English with the evidence for each finding, the fixes already made and whatever is left for you to decide.
Do you use AI in your security work?
Yes. BY BANKS is verified under Anthropic's Cyber Verification Program at the Defense Access tier, so we can use its most advanced models to find weaknesses faster, and each finding is still confirmed by an engineer before it reaches you.
Do you fix what you find?
Yes, and that is the difference. The engineers who find a weakness can close it, test it again and show you the proof.